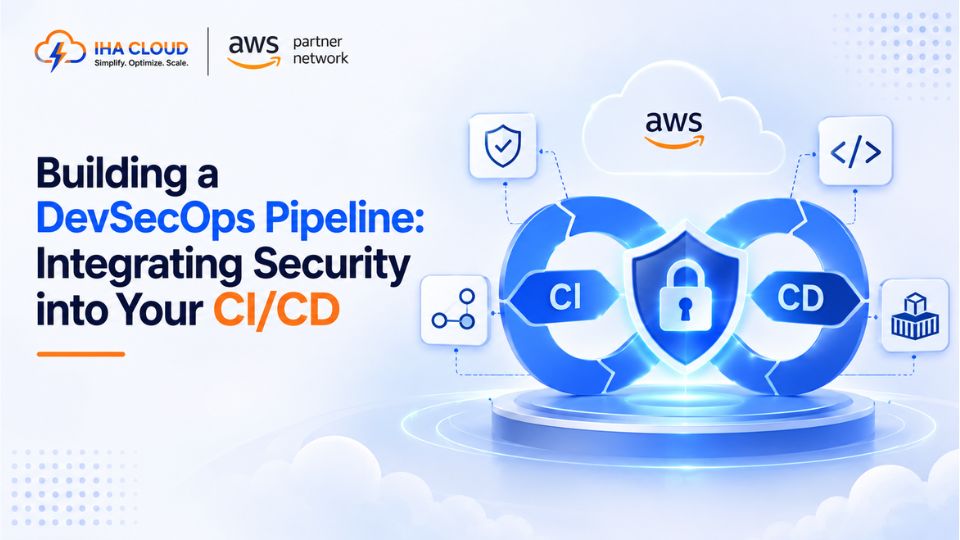
Building a DevSecOps Pipeline: Integrating Security into Your CI/CD
Security reviews that happen after code is already deployed catch problems too late, and usually too slowly to matter. DevSecOps means moving those checks earlier — into the pipeline itself — so vulnerabilities are caught before they ever reach production. What Changes With DevSecOps Traditional workflows treat security as a separate, later step. DevSecOps treats it as part of the same pipeline that builds and tests the code, running automatically on every change. Where Security Checks Fit in the Pipeline A Practical Pipeline Order Keeping It From Slowing the Team Down Common Mistakes The Real Goal DevSecOps is not about adding more steps for their own sake — it is about making sure security scales at the same pace as deployment frequency. A team deploying multiple times a day needs security checks that run automatically every time, not a manual review that can only happen occasionally.
Building a DevSecOps Pipeline: Integrating Security into Your CI/CD Read More »